PRESS RELEASE
WAY Systems and TNS Add PIN Debit Capabilities for Synapse Customers
TNS 16.69, +0.25, +1.5%) has teamed up with WAY Systems to offer PIN Debit capabilities to mobile merchant customers via Synapse sm, TNS' wireless payment gateway.
Based in Boston, MA, and founded in 2004, WAY Systems is a privately held organization that provides mobile Point of Sale (POS) terminal devices to mobile merchants throughout the US. WAY Systems currently offers the smallest, most compact terminal models available.
Since 2005, WAY Systems has utilized the Synapse solution by TNS to process credit card transactions over TNS' secure global network. Once implementation is complete, Synapse customers utilizing WAY terminal devices will be able to process both debit and credit transactions over the TNS payment gateway.Harry Hargens, Vice President of Product Management at WAY Systems said: "Synapse customers using WAY terminals will now enjoy the benefits of utilizing a single solution for both credit and PIN Debit. TNS and WAY Systems are able to offer the complete package of reliable service and quick and easy processing from anywhere through one secure wireless connection.
"We have a long standing relationship with TNS and the service they have delivered has proven to be extremely reliable, so it just made sense for us to build on that trusted relationship.
"Merchants already using our terminals and the Synapse payment gateway for credit transactions will be able to instantly use the same devices for debit processing once the solution is available. By working with TNS, we are able to offer the combination of a secure mobile merchant solution along with the reliable service TNS brings to the table."
The Synapse solution offered by TNS provides a one-stop-shop for ISOs, acquirers, and processors to manage wireless terminal portfolios.
By taking advantage of Synapse, merchants are able to rely on the security and performance of TNS' PCI DSS certified Synapse processing environment and 24x7x365 helpdesk services with live real-time support.
Alan Schwartz, Executive Vice President, North America Sales at TNS, added: "We are thrilled to be expanding our processing capabilities with WAY Systems. Having the ability to process debit transactions rounds out our feature-set, and will allow customers to take a deeper look at the high quality of customer service and gateway reliability that sets us apart from our competitors."
Synapse is a wireless gateway and management solution providing services for ISOs, acquirers, and processors to manage their wireless terminal portfolios. Using a PCI DSS certified processing environment, it offers a broad range of end-to-end services. The solution includes wireless network access, account activation, fast, reliable, and secure transaction delivery to most major processors, web-based merchant and terminal management, customizable online reporting, and live 24x7 customer service.
To find out more about TNS, please visit www.tnsi.com.
About Transaction Network Services
Transaction Network Services (TNS) is an international data communications company that enables payments, money and voices, to move around the world.
TNS' mission is to enable the world to transact. It does this through a broad range of networking, communications and value added services, which it provides to many of the world's leading retailers, banks/processors, telecommunications companies and financial markets.
Since its inception in 1990, TNS has designed and implemented multiple data networks, each designed specifically for the transport of transaction-oriented data. TNS' networks support a variety of widely accepted communications protocols and are designed to be scalable and accessible by multiple methods. Today, TNS has offices throughout the world serving customers in 28 countries with the ability to provide services in other countries.
For further information about TNS, visit www.tnsi.com
Statements and information contained in our press releases and newsletters that are not descriptions of historical fact may contain forward-looking statements. Forward-looking statements involve a number of risks, uncertainties or other factors beyond our control, which could cause actual results to differ materially from historical results or performance and from any opinions or statements expressed with respect to future periods. www.tnsi.com
SOURCE: Transaction Network Services
TNS
Clare Cockroft
PR Manager, +44 (0)114 292 6416
ccockroft@tnsi.com
or
Stephen Aryan, +44 (0)114 292 6410
PR Assistant
saryan@tnsi.com
Thursday, April 16, 2009
Way Systems and TNS Add PIN Debit to Synapse Customers
Phish-Ingcreases
Banking / Finance News -
Source: ComputerWeekly
Banks, online payment organizations and other financial institutions are bearing most of the financial cost of phishing attacks, according to research firm Gartner.
A survey of nearly 4,000 US consumers revealed a 40% increase in the number of phishing victims in 2008 over the year before to five million.
The average loss was $350 per phishing attack, but consumers said they had recovered 56% of their losses from the financial institutions involved.
"The findings underline the fact that the war against phishing is far from over," said Avivah Litan, analyst at Gartner.
Celent Report on AltPays
Alternative Realities: The Commoditization and Allure of Alternative Payments
Report Published by Celent
In the past three years, alternative payments have gained considerable market value with no loss of momentum in sight. Alternative payments currently account for roughly 15% of total e-commerce volume. However, by offering a superior value proposition to buyers, alternative payments pose a threat to traditional payment methods. PayPal's recent acquisition of Bill Me Later validates Celent's assessment that the strongest value is derived from the creation of sales lift.
In less than a decade, alternative payments have evolved from "dot bomb" burnouts to widely accepted, widely recognized forms of online payment. Alternative players' business models once relied on their solutions' status as "something new" or the only way to pay in a particular online environment. However, they now focus on providing greater value than payment cards. Card brands and issuers stand to forgo $345 million in volume in 2010 and about $1.7 billion in volume in 2015 to alternative payment. In a new report, Alternative Realities: The Commoditization and Allure of Alternative Payments, Celent examines the maturation of the online alternative payments sector.
Given cards' historical dominance over online payments, this market is the card industry's to lose. Every time a bank account is debited via ACH rather than a card, the card industry loses roughly 1.5 - 2.4% or more of the transaction size. The card industry must pay attention to alternative payments, which can be categorized as enablers, quasi-disruptors, or disruptors, in order to prevent further losses.
Enablers offer a technological "wrap around" for payment cards that leads to increased card volume when cards are used as the source of funds. Quasi-disruptors are players that allow for both cards and other funds sources (e.g., bank accounts) to be used. Should bank accounts be used instead, these same players take on disruptive qualities. Finally, disruptors are solutions in which the card industry plays no role whatsoever.
However, the outlook is not entirely rosy for alternative payments. "Alternative payments players have already become commodities in terms of security, convenience and pricing. The real differentiator is their ability to induce purchases and affect a corresponding sales lift. Of all the major alternative payments players, Bill Me Later understands this the best," says Red Gillen, senior analyst with Celent's banking group and author of the report. "The greatest threat to the card industry is a disruptive alternative payments solution that has figured out how to increase online merchants' sales. With its recent acquisition of Bill Me Later, PayPal is obviously a believer in this fact."
"The spoils will go to those players who understand that their role is no longer simply making shoppers able to pay. Instead, such players realize that, going forward, they must make shoppers want to pay," he adds.
This report spotlights some of the main players in the remittance space and provides an analysis of how they match up against online payment incumbents (cards) as well as each other.
The report contains 56 pages, 17 figures and 10 tables. A table of contents for this report is available online.
Members of Celent's Retail and Business Banking research service can download the report electronically by clicking on the icon to the left. Non-members should contact info@celent.com for more information.
About Celent
Celent is a research and advisory firm dedicated to helping financial institutions formulate comprehensive business and technology strategies. Celent publishes reports identifying trends and best practices in financial services technology and conducts consulting engagements for financial institutions looking to use technology to enhance existing business processes or launch new business strategies. With a team of internationally experienced analysts, Celent is uniquely positioned to offer strategic advice and market insights on a global basis. Celent is a member of the Oliver Wyman Group, which is part of Marsh & McLennan Companies [NYSE: MMC].
Signature Debit in a Chip and PIN World
Why Your Credit Card Might Not Work Overseas - SmarterTravel.com
Ed Perkins on Travel
by Ed Perkins - April 16, 2009
The next time you go overseas—especially to Europe—don't be surprised if you have occasional trouble using your credit card. Many big European banks have switched to chip-enabled cards that require use of an identification number (PIN) to complete the transaction, and only a very few cards issued in the United States comply with the new European standard. International card networks (American Express, MasterCard, and Visa) require all participating merchants to accept U.S. cards, and many do. But you may still face situations where your card won't work.This column was suggested by reports of difficulties experienced by American travelers in Europe. Several reported having their cards refused by a local hotel, restaurant, or merchant unless the travelers provided a PIN. After the usual argument, some accepted the American card; others didn't. The worst case came from an American traveling in Scandinavia, who tried to buy a rail ticket with his Visa card from a vending machine in a small-town station that did not have an attendant. He was flat unable to buy a ticket and had to prevail on some helpful local to buy it for him.
Advertisement
After checking with the card networks and a few banks, I've concluded that the U.S. card establishment really doesn't have a foolproof solution to the problem. Here's what they say:
* The party line is that there's no problem: Your U.S.-issued card is good everywhere with a signature and without a PIN. Even though some parts of the world have adopted chip-enabled systems—requiring a PIN—as a means of authentication, magnetic-stripe cards issued in the United States continue to be accepted everywhere the card is accepted, including countries that have adopted chip-and-PIN technology. Most terminals in those countries can recognize a non-chip-enabled card and will indicate when a signature, rather than PIN, is necessary.
Continue Reading Ed's column at SmarterTravel
Wednesday, April 15, 2009
280 Million Records Compromised Last Year
Damning report finds simple steps still being ignored
Phil Muncaster - vnunet.com, 15 Apr 2009
More than 280 million records were compromised in 2008, according to a new Data Breach Investigations Report from global comms and IT provider Verizon Business.
The report was written by the Verizon Business Risk team using first-hand evidence collected from the firm's data breach investigations over 2008.
Advertisement
Three-quarters of breaches resulted from external threats, the report found, while just 20 per cent were caused by insiders. This is despite the message from most security firms that the inside threat is more dangerous than that posed from the outside.
The sheer number of credit card and other details being compromised has driven their price down on the underground economy, forcing criminals into new tactics, explained Matthijs van der Wel, managing principal of forensics at Verizon Business.
The average price for a piece of stolen card information has dropped from around $10 (£6.70) in 2007 to 50 cents (33p) today.
"For the criminals it's becoming less profitable so they're looking for new ways to make money, which means targeting financial institutions much more, looking for richer data," said van der Wel.
"Attackers have to do a lot more work to get their information now. They're intercepting the PINs, which has been theorised before but now we're seeing it. " To this end, criminals are creating customised 'memory scraping' malware to harvest customer PINs entered at ATMs from banks' servers.
Yet despite the increasingly creative ways some criminals are compromising customer data for sale on the black market, the majority of incidents appear to have been preventable, according to the report. For example, 81 per cent of affected organizations subject to the Payment Card Industry Data Security Standard were found to be non-compliant prior to being breached.
Editor's Note: HomeATM is PCI 2.0 PED Compliant!
A software application can never ever be certified because it would be literally impossible to know what malware may lurk in the darkness of each individual PC. Since a software application would use the PC, the keyboard, or the mouse...as the PIN Entry Device (PED) every single PC would need to be PCI PED certified.
Since only 24 devices have been 2.0 certified worldwide and only 1 (HomeATM) designed for eCommerce, I would say that a software application being awarded PCI 2.0 PED certification is "impossible."
Some 53 per cent of stolen data records came from organizations using shared or default credentials, and 83 per cent of hacks were considered avoidable through simple or intermediate controls. Van der Wel recommended firms to check access controls regularly, change default credentials, keep up to date with patches, and test applications for vulnerabilities. "You need to ask yourself 'Do I need to store this data?'" he said. "Many organisations today are data hungry, but if you don't store the data you'll reduce your risk."
If Cybercriminals Focus on PIN's, Shouldn't We Focus on Security?
Description: Hackers stole 285 million electronic records in 2008, more than in the previous four years combined, with the vast majority of breaches targeting the financial services industry, according to a study from Verizon.
Lat year Verizon investigated 90 breaches with 285 million records stolen, of which 93% were accounted for by the financial sector. The industry also accounted for 30% of the breaches - double its share for 2007.
Verizon says the increase reflects the recent trends in cybercriminal activity, especially the focus on acquiring PIN numbers to sell on the black market.
Editor's Note: If there's a FOCUS on acquiring PIN numbers to sell on the black market, then "SECURITY" needs to be the financial sector's FOCUS. Again...92% of all breaches are software-based (see graph...top left) and if cybercriminals are "focusing" on obtaining PIN's take an "educated guess" as to which one will be targeted.
Between the Graph above and the Graph-itti on the right...the writing is "so on the wall" and it's clearly showing us the future.
I KNOW I'm not the only one who see's it!
93% of breaches target financial sector, 92% target software...and 90% of attacks come from organized crime) Leave your comment below on the 93/92/90 data...
The story continues: Organized crime was responsible for (90%) nine in 10 breaches, with an explosion of attacks targeting PIN data, which Verizon says hit the consumer much harder than typical signature-based counterfeit attacks.
The higher monetary value commanded by PIN data has spawned a cycle of innovation in attack methodologies, with criminals re-engineering their processes and developed new tools, such as memory-scraping malware, to steal this valuable data.
Editor's Note: Click the memory-scraping malware link to read more into the future of software based PIN Debit at Wired.
Will V/MC Flip the KillSwitch on Interac?
With lucrative banking fees in their sights, Visa and MasterCard aim to challenge a home-grown success
THERESA EBDEN
April 15, 2009
With the debate raging in Ottawa about credit card rates, you may have overlooked another issue in the mix: the uncertain future of your bank debit card.
Let's put it this way. Don't get too used to calling your debit transactions "Interac," because Visa Canada and MasterCard Canada may yet challenge the monopoly held by the national not-for-profit Interac Association, a co-operative payment system created in 1984 by the country's big banks and merchants.
Many Canadians don't realize that Interac is a low-cost anomaly.
In other countries, high-fee, for-profit systems from companies such as Visa, MasterCard and China UnionPay reign. Now the first two are considering a foray into Canada. Visa has held talks with Canadian banks and retailers, said Tim Wilson, head of Visa Canada. Visa debit is used by 844 million cardholders in 170 countries, according to company reports.
"The bank card in Canada has been tremendously successful, but it's relatively plain vanilla," Mr. Wilson said.
MasterCard said recently it will "create competition in the Canadian debit market where it has never existed" with its debit system, Maestro, used by 652 million people in more than 100 countries. Under the system, Canadian customers could use their debit cards abroad, and retailers here could accept foreign cards.
Interac is in a fight for its life, says Mark O'Connell, its president and CEO. He maintains it is a world-class, low-cost payment system that won't survive unless its regulatory structure is altered by the Competition Bureau.
Interac should be "a more independently run commercial organization that has the ability to innovate," he said. As it stands, the not-for-profit association can't raise funds for research and development of new products, such as high-tech terminals.
"We cannot let such a successful debit system continue in this shackled fashion, as the market changes around it," Mr. O'Connell said. "I think it would be a tragedy to have this made-in-Canada success story obviated by U.S. card companies."
Analysts say that Visa and MasterCard can enter Canada with new products and set up lucrative fee structures for all involved - themselves, the banks, and the middlemen.
Continue Reading
PIN Crackers
By Kim Zetter Email
Hackers have crossed into new frontiers by devising sophisticated ways to steal large amounts of personal identification numbers, or PINs, protecting credit and debit cards, says an investigator. The attacks involve both unencrypted PINs and encrypted PINs that attackers have found a way to crack, according to the investigator behind a new report looking at the data breaches.
"We're seeing entirely new attacks that a year ago were thought to be only academically possible," says Sartin. Verizon Business released a report Wednesday that examines trends in security breaches. "What we see now is people going right to the source ... and stealing the encrypted PIN blocks and using complex ways to un-encrypt the PIN blocks."
The revelation is an indictment of one of the backbone security measures of U.S. consumer banking: PIN codes. In years past, attackers were forced to obtain PINs piecemeal through phishing attacks, or the use of skimmers and cameras installed on ATM and gas station card readers. Barring these techniques, it was believed that once a PIN was typed on a keypad and encrypted, it would traverse bank processing networks with complete safety, until it was decrypted and authenticated by a financial institution on the other side.
But the new PIN-hacking techniques belie this theory, and threaten to destabilize the banking-system transaction process.
according to the 2009 Data Breach Investigations report, the hacks have resulted in "more targeted, cutting-edge, complex, and clever cybercrime attacks than seen in previous years."
"While statistically not a large percentage of our overall caseload in 2008, attacks against PIN information represent individual data-theft cases having the largest aggregate exposure in terms of unique records," says the report. "In other words, PIN-based attacks and many of the very large compromises from the past year go hand in hand."
Although there are ways to mitigate the attacks, experts say the problem can only really be resolved if the financial industry overhauls the entire payment processing system.
"You really have to start right from the beginning," says Graham Steel, a research fellow at the French National Institute for Research in Computer Science and Control who wrote about one solution to mitigate some of the attacks. "But then you make changes that aren't backwards-compatible."
PIN hacks hit consumers particularly hard, because they allow thieves to withdraw cash directly from the consumer's checking, savings or brokerage account, Sartin says. Unlike fraudulent credit card charges, which generally carry zero liability for the consumer, fraudulent cash withdrawals that involve a customer's PIN can be more difficult to resolve since, in the absence of evidence of a breach, the burden is placed on the customer to prove that he or she didn't make the withdrawal.
Some of the attacks involve grabbing unencrypted PINs, while they sit in memory on bank systems during the authorization process. But the most sophisticated attacks involve encrypted PINs.
Sartin says the latter attacks involve a device called a hardware security module (HSM), a security appliance that sits on bank networks and on switches through which PIN numbers pass on their way from an ATM or retail cash register to the card issuer. The module is a tamper-resistant device that provides a secure environment for certain functions, such as encryption and decryption, to occur.
According to the payment-card industry, or PCI, standards for credit card transaction security, PIN numbers are supposed to be encrypted in transit, which should theoretically protect them if someone intercepts the data.
The problem, however, is that a PIN must pass through multiple HSMs across multiple bank networks en route to the customer's bank. These HSMs are configured and managed differently, some by contractors not directly related to the bank.
At every switching point, the PIN must be decrypted, then re-encrypted with the proper key for the next leg in its journey, which is itself encrypted under a master key that is generally stored in the module or in the module's application programming interface, or API.
"Essentially, the thief tricks the HSM into providing the encryption key," says Sartin. "This is possible due to poor configuration of the HSM or vulnerabilities created from having bloated functions on the device."
Sartin says HSMs need to be able to serve many types of customers in many countries where processing standards may be different from the U.S. As a result, the devices come with enabled functions that aren't needed and can be exploited by an intruder into working to defeat the device's security measures. Once a thief captures and decrypts one PIN block, it becomes trivial to decrypt others on a network.
Other kinds of attacks occur against PINs after they arrive at the card-issuing bank Once encrypted PINs arrive at the HSM at the issuing bank, the HSM communicates with the bank's mainframe system to decrypt the PIN and the customer's 16-digit account number for a brief period to authorize the transaction.
During that period, the data is briefly held in the system's memory in unencrypted form.
Sartin says some attackers have created malware that scrapes the memory to capture the data.
"Memory scrapers are in as much as a third of all cases we're seeing, or utilities that scrape data from unallocated space," Sartin says. "This is a huge vulnerability."
He says the stolen data is often stored in a file right on the hacked system.
"These victims don't see it," Sartin says. "They rely almost purely on anti-virus to detect things that show up on systems that aren't supposed to be there. But they're not looking for a 30-gig file growing on a system."
Information about how to conduct attacks on encrypted PINs isn't new and has been surfacing in academic research for several years. In the first paper, in 2003, a researcher at Cambridge University published information about attacks that, with the help of an insider, would yield PINs from an issuer bank's system.
The paper, however, was little noticed outside academic circles and the HSM industry. But in 2006, two Israeli computer security researchers outlined an additional attack scenario that got widespread publicity. The attack was much more sophisticated and also required the assistance of an insider who possessed credentials to access the HSM and the API and who also had knowledge of the HSM configuration and how it interacted with the network. As a result, industry experts dismissed it as a minimal threat. But Steel and others say they began to see interest for the attack research from the Russian carding community.
"I got strange Russian e-mails saying, Can you tell me how to crack PINs?" Steel recalls.
But until now no one had seen the attacks actually being used in the wild.
Steel wrote a paper in 2006 that addressed attacks against HSMs as well as a solution to mitigate some of the risks. The paper was submitted to nCipher, a British company that manufactures HSMs and is now owned by Thales-eSecurity. He says the solution involved guidelines for configuring an HSM in a more secure manner and says nCipher passed the guidelines to customers.
Steel says his solution wouldn't address all of the types of attacks. To fix the problem, would take a redesign.
But he notes that "a complete rethink of the system would just cost more than the banks were willing to make at this time."
Thales-eSecurity is the largest maker of HSMs for the payment-card and other industries, with "multiple tens of thousands" of HSMs deployed in payment-processing networks around the world, according to the company. A spokesman said the company is not aware of any of the attacks on HSMs that Sartin described, and noted that Thales and most other HSM vendors have implemented controls in their devices to prevent such attacks. The problem, however, is how the systems are configured and managed.
"It's a very difficult challenge to protect against the lazy administrator," says Brian Phelps, director of program services for Thales-eSecurity. "Out of the box, the HSMs come configured in a very secure fashion if customers just deploy them as is. But for many operational reasons, customers choose to alter those default security configurations — supporting legacy applications may be one example — which creates vulnerabilities."
Redesigning the global payment system to eliminate legacy vulnerabilities "would require a mammoth overhaul of virtually every point-of-sale system in the world," he says.
Responding to questions about the vulnerabilities in HSMs, the PCI Security Standards Council said that beginning next week the council would begin testing HSMs as well as unattended payment terminals. Bob Russo, general manager of the global standards body, said in a statement that although there are general market standards that cover HSMs, the council's testing of the devices would "focus specifically on security properties that are critical to the payment system." The testing program conducted in council-approved laboratories would cover "both physical and logical security properties."
Software Based PIN...Doin' It Wrong?
Secure Software Development Programs are Rare
Survey by Forrester Consulting and Veracode shows businesses struggling to stay on top of application security
Apr 14, 2009 | 03:20 PM
By Kelly Jackson Higgins
DarkReading
If you still don't think security vulnerabilities in software will necessarily catch up with you, think again: 62 percent of organizations in the last 12 months suffered data breaches as a result of bugs being exploited in their major applications, according to a newly released survey.
Forrester Consulting, commissioned by Veracode, surveyed application developers and security and risk professionals in 200 organizations in the U.S. and U.K., and found that secure software development programs are rare -- only 34 percent said they have a software development lifecycle program that integrates security.
"The survey showed that people, process, and culture are the primary inhibitors," says Matt Moynahan, CEO of Veracode, in an interview. "Security is not a core competence of enterprises developing code."
Continue DarkReading
How to Hack an ATM Part IV
By Amy Dale
April 15, 2009 06:05am
POLICE are searching for three men seeing running from an ATM explosion in Lane Cove early today. The explosion occured outside the National Australia Bank in Longueville Road at about 2am.
The ATM was badly damaged_ with debris strewn around the footpath_ however no cash was stolen.
Witnesses reported seeing two men sprint from the scene of the blast into a car driven by a third man but a police search failed to locate them.
Detectives from Strike Force Piccadilly, which was established following a string of ATM blasts across the state, were called to the scene.
NAB ATMs were the targets of two successful bamraids in St Ives and Neutral Bay in February.
Tuesday, April 14, 2009
If HomeATM is "Doin' It Right" Who's "Doin' It Wrong?"

The Green Sheet April 13, 2009 o Issue 09:04:01 (click graphic to enlarge or read below)
Doin' it right
POS equipment continues to get smaller, cheaper and faster. In March 2009, Montreal-based payment hardware and software provider, HomeATM ePayment Solutions, rolled out Safe-T-PIN, the first Internet POS PIN entry device (PED) to achieve Payment Card Industry (PCI) Data Security Standard (DSS) PED 2.0 certification. "What Safe-T-PIN is all about is very simple," said Mitchell Cobrin, Chief Operating Officer of HomeATM.
"All we've done is to replicate a POS device within PCI standards for home use. "Our goal is to have our product with every small e-merchant and in every household of online consumers, and we're talking a couple of hundred million people."
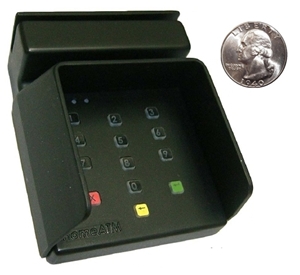
Safe-T-PIN is a ready-to-use, pocket-sized universal serial bus (USB) "plug and play" device that requires no software upgrades, works with any operating system or Web browser, eliminates the need for keying in card numbers because the card is swiped, and works with any bank, processor or currency. It is also Europay, Visa Inc. and MasterCard Worldwide compliant to accommodate smart cards, magstripes or chip and PIN technology.Transactions for the masses
"Safe-T-PIN gives everyone – merchants and consumers alike - the ability to do a transaction that is more secure than any they could do in a card-not-present environment, including debit and credit card transactions and P2P [person-to-person] money transfers in real time," Cobrin said. "Consumers swipe their cards, enter their password for a PIN debit, and it goes through the EFT [Electronic Funds transfers] network in the same amount of time as a brick-and-mortar transaction - and it's fully encrypted. We're not inventing a system because it's really the mirror image of the POS EFT experience. All we're doing is making it accessible to home-based, online merchants and consumers."
According to many payments industry experts, the biggest problem with e-commerce is the lack of consumer confidence in the ability to make purchases or send money online securely. They cannot see e-commerce merchants face to face and hesitate to fully trust them.
To address consumer fears about identity theft, lack of brand recognition, malware and keystroke monitoring, HomeATM has a newsletter and blog that offer viable solutions to these common concerns.
"Safe-TPIN really speaks to the heart of this matter because it makes all of that totally impregnable," Cobrin said.
Disposable POS
Additionally, HomeATM has made Safe-TPIN cost effective for the smaller and midsized e-commerce merchants, as well as for those merchants with employees who take electronic payments off site. "Safe-T-PIN's price almost pegs this unit as a disposable POS device, so if it's stolen, if it's discarded or disappears, you haven't lost the hundreds of dollars it would cost to replace it," Cobrin said. "We remove the notion of $30 a month leases on systems for merchants struggling in today's economy."Partnership power
HomeATM has a minimal direct sales force; the company's preference is to support the ISO reseller channel and stay in the background. "We really respect and appreciate the role that the ISO can play," Cobrin said. "They're the frontline people who have the expertise in the industry, so we're here to support any particular initiatives that they might be working on to assist them in marketing this product." Cobrin noted that in the past year same-store sales have steadily declined, and e-commerce is eroding business at brick-and-mortar locations, which has created a tremendous opportunity for ISOs and merchant level salespeople to put POS devices in the hands of merchants who would not otherwise be able to contemplate having merchant processing accounts.
"Tomorrow's e-retail and P2P remittance commerce is going to happen with or without those merchants who choose not to participate," Cobrin said. "And we're not trying to cannibalize brick-and-mortar as much as we want to give all merchants, regardless of size, the opportunity to change a fairly antiquated type of thinking and not be a dinosaur.
"There are so many different approaches because a POS of this nature has never existed, so I think new markets are just inherently going to be developed in ways that, perhaps, our team has not yet even contemplated."
EDITOR'S NOTE: So...if HomeATM is "Doin' it Right" then who's "Doin' It Wrong?"
Excerpts from a story from American Banker:
Acculynk Inc. says its Internet PIN debit service...PaySecure enables consumers to enter their PIN with a mouse on a virtual PIN pad that appears on the computer screen during checkout.
"I would highly recommend [to any consumer] not entering their PIN anywhere on the Internet unless it was hardware-based," she said.
But Ashish Bahl, Acculynk's CEO said the networks involved with the pilot tests have little concern about the security of PaySecure.
In an e-mail last week, McGuire wrote that Pulse believes that "Internet-based PIN debit has tremendous potential value for consumers, as well as for merchants and debit card issuers."
Editor's Note: It would have even "more tremendous-er" (sic) value if it was a "TRUE" internet based PIN Debit application, but...since the "card's not present" either is TRUE PIN Debit. (see "Software PIN Debit Doesn't Exist...)
Javelin's (Bruce) Cundiff said that "a substantial subset of consumers" are "making the behavior change from credit cards to other methods of payment" and that they would benefit from another "pay-now" method.
(Editor's Note: Metavante isn't Metavante anymore. It's FIS. Which reminds me...if you're going to the ETA, make sure and stop by FIS' booth, which they are sharing with HomeATM...and utilizing to push HomeATM's "True" PIN Debit platform. Oh...and while you're there, you can congratulate them on their recent acquistion of Metavante...and therefore...NYCE!) See NYCE! Metavante Acquired by Fidelity National
Penny for your card...$1000 for your PIN
JORDAN ROBERTSON - The Associated Press
SAN FRANCISCO (AP) — SAN FRANCISCO (AP) One economy apparently isn't hurting these days, the one run by identity thieves in the dark corners of the Internet.
Demand and prices remain stable for stolen credit cards, Social Security numbers and other private information, according to a new study by security software maker Symantec Corp.
Meanwhile, the supply of such data is steady too, thanks to the way the recession has inspired new scams targeting people who are worried about work and their finances, according to the Symantec report and another study from Gartner Inc. that was due to be released Tuesday.
"There's no pricing pressure at all, it's not dropping, they're not negotiating down," said Alfred Huger, vice president of Symantec Security Response. "That tells us that there are still the same number of buyers. The underground economy has not been affected by the recession."
One reason is that the prices for some records have been falling for years and can't go much lower. Stolen credit card numbers now go for as little as 6 cents each, if they're bought 10,000 at a time. The price can be $30 per card for smaller orders. Access to hijacked e-mail accounts: 10 cents to $100.
Bank account credentials: $10 to $1,000.
Editor's Note: Guess which one is $1,000? Right...bank account credentials with the PIN Number. See chart on left. So how do hackers get their hands on PIN numbers? Through a PCI 2.0 PED which 3DES encrypts the Track 2 data, and utilizes DUKPT key management, or a software platform? Hmmmm. Tough one.
Scammers can hire people to "cash out" compromised bank accounts for between 8 percent and 50 percent of the amount they're stealing. Hosting for scam Web sites ranges from $3 to $40 per week.
Continue Reading
You Wormy Little Twit!
First from PC World: It looks like Twitter's website has been scrubbed clean after several bouts of the "Mikeyy" or "StalkDaily" wormplagued the service. Even though the threat seems to have passed,questions remain about just how serious this attack was and if therewill be any repercussions for the worm's creator.
Worm Attacks Bird
Early on Saturday, April 11, the Mikeyy worm started to spread viaTwitter posts by encouraging you to click on a link to a rivalmicro-blogging service StalkDaily.com. As soon as you clicked on thelink your account would be infected and begin to send out similarmessages encouraging your followers to visit StalkDaily. Then yourfollowers would become infected and the worm's infection rate wouldgrow. You could also catch the worm by viewing infected profiles onTwitter.com.
Description:
What on earth is going on at Twitter? That's the question that many people will be asking after the Easter break, following a wave of cross-site scripting worms that hit the micro-blogging site. After each attack Twitter said that it had resolved the problem, only for hackers to return hours later with another attack effectively rubbing Twitter's nose in it.
The latest cross-site scripting worm we've seen on Twitter urges the website to hire Mikeyy Mooney, the suspected author of at least the earlier attacks and give a phone number. Journalists who have spoken to 17-year-old Mooney have confirmed to Sophos that the phone number used in the latest worm messages is genuine.
We've chosen to obscure the phone number, although it is trivial for anyone to discover it if they search on the Twitter site for archived messages. If Mooney is responsible for the worms that have troubled Twitter and its many users today then the correct course of action is for the authorities to investigate - not for the internet community to take the law into its own hands.
Of course, it's understandable that some may feel very aggrieved by a worm messing with their Twitter profile settings but it's up to Twitter to decide if it wants to make a complaint to the police.
But the worm suggesting that Mikeyy could help Twitter out with its security problems wasn't the end of it.
Yet another cross-site scripting worm hit Twitter, pretending to be a link to removal instructions for the earlier attacks. Unfortunately, if you clicked on the bit.ly link you were redirected to an infected Twitter profile page, which - yes, you guessed it - would infect your profile too and continue the spread of the worm.
What's most alarming to me though is that it seems Twitter was caught with its pants down in the aftermath of all of these attacks. To be hit by one cross-site scripting worm may be regarded as a misfortune, to be struck three or four times over a weekend looks like carelessness.
Heartland Breach Still Affecting Consumers
Thieves use stolen data on debit, credit transactions
BY DENEEN SMITH
dsmith@kenoshanews.com
Customers at Southport Bank in Kenosha fell victim last week to a data breach at a company that processes debit and credit card transactions for national retailers.
In January, Heartland Payment Systems announced a data breach. Since then, customers of more than 600 banks around the country have been victims of debit card fraud, with thieves using data stolen during the Heartland breach.
Last week, Southport learned 78 customers had been hit by debit card theft, with the thieves using fraudulently produced duplicate cards to make purchases. The bank said that customers — including several Southport Bank employees — began noticing irregular transactions on their accounts April 8th. Other local banks also have been affected, including Bank of Kenosha.
Southport senior vice president Gregg Pfarr — who said his own personal account was one of those breached — said the bank moved to shut down the fraud, issuing new cards to customers believed vulnerable and placing a $100 limit on signature-only uses of debit cards that do not require customers to provide a personal identification number (PIN). Editor's Sarcastic Note: That must mean that PIN transactions are more secure than signature debit...who woulda thunkit?
Before the bank was alerted to the scam, the identity thieves made $31,000 in purchases with the cards. Southport Bank is covering those losses; bank customers are not liable for the charges. According to Pfarr, the problem is related to the security breach announced by New Jersey-based Heartland, which provides debit and credit card processing services for more than 250,000 retailers across the country.
Heartland issued statements saying it had uncovered “malicious software” planted in the company’s payment network. That software apparently captured data from the magnetic strip on the back of credit and debit cards, allowing thieves to recreate the cards. The breach may have exposed millions of cardholders across the nation to fraud. According to Heartland, the malicious software did not capture individual PINs, addresses or other personal information from card holders. The FBI is investigating the breach.
Pfarr said it appears scammers are using the information to hit banks in clusters. He said the fraudulent charges on customers’ cards were out of state, concentrated in Arizona, California and Illinois. Pfarr said the charges on his own account were at Wal-Mart and Walgreens stores in Arizona. The charges to Southport customers all appeared to occur in the last week, and the bank now believes it has shut down all the cards vulnerable to the fraud.
Bank of Kenosha officials acknowledged the Heartland breach also affected their bank. However, chief financial officer Mark King said he could not comment on the details, saying the bank officer who worked on the issue was out of the office Monday. Pfarr said all consumers should keep a close watch on account information and be wary of fraudulent charges. By law, he said, customers are not liable for fraudulent purchases on their cards.
More on the Paradigm Shift...eCommerce vs. Brick-and-Mortar Sales
Online shopkeepers willing to indicate how theirsales were doing in 2009 generally reported extremes, with sales eitherrising or falling by more than 10 percent, according to a new PracticaleCommerce survey.
Practical eCommerce asked a group of its readers how their 2009sales had fared compared to the first quarter of 2008. By April 7,2009, 34.6 percent of those responding had seen a 10 percent or greaterincrease in sales for the first three months of 2009 compared to thesame 2008 quarter. Some individuals indicated sales growth of 30percent or more. Unfortunately, another 28.8 percent of respondentssaid that their sales had fallen 10 percent or more in the first threemonth of 2009 compared to the same 2008 period. One merchant said saleswere off by more than 50 percent.
The Trend Could be Related to Business Size
The extremes in ecommerce sales growth and decline could simply be afunction of the fact that most Practical eCommerce readers representsmall-to medium-sized ecommerce businesses, which may be more volatilethan larger concerns. As evidence of this, a survey conducted inNovember 2008 by Practical eCommerce discovered that 47.7 percent ofits readers were relatively small businesses with sales of less than$100,000 annually; 23 percent had annual sales of $100,000 to $500,000;and another 18.7 percent had yearly sales between $500,000 and $5million.Smaller ecommerce businesses can be more volatile because of tightercash flows, smaller marketing budgets, and just because of the size oftheir total revenues.
"Due to the economic situation, I've put off purchasing replacementinventory and new inventory. I also put off attending the NYC Toy Fairwhich is 'the' show to attend in my industry," said one retailer whosesales had fallen 52 percent compared to the first quarter of 2008.
When sales drop for smaller retailers there is rarely a largereserve of capital. Cash flow constricts and even vital businessfunctions like purchasing inventory get postponed. When a product isout of stock, it cannot be sold, and sales fall. Tight budgets can alsomean that smaller merchants are likely to stop advertising before theirlarger cousins, again leading to a dramatic decline in total sales.
The Trend Could Be Tied to Brick-and-Mortar Sales
A second potential reason for the dual trends could be related tobrick-and-mortar sales. Nearly one fifth of Practical eCommerce readersoperate both a physical retail outlet and an online store. Sales atso-called brick-and-mortar stores are generally believed to be trailingecommerce sales, meaning that some of the survey's respondents might beweighed down with lackluster location sales and fixed, brick-and-mortaroverhead."Brick-and-mortar sales are stagnant," said one respondent. "The[economic] 'atmosphere' has kept customers away from in-storeshopping," said another survey respondent." Those who do shop makepurchases and then have them shipped to their residence to keep theirpurchases on the 'down-low' from the public eye."
The Trend Could Be Industry Related
The seemingly extreme differences in how well an ecommerce businesswas doing in 2009 might also have been the result of which industry amerchant was serving. As an example, of those businesses that hadexperienced a 10 percent or more growth in sales in the first quarterof 2009, 22 percent were in the home, furniture, or garden segment.As one retailer pointed out, more customers might be looking fordo-it-yourself supplies, and they are finding them cheaper online.
No Clear Resolution
Unfortunately, the survey tended to raise more questions than itanswered. But it was clear that in spite of almost constant concernsabout the economy several merchants are experiencing sales growth.The ATM Skimming/Romania Connection
A high-tech syndicate composed mainly of Romanians is believed to be behind a spate of recent ATM skimming incidents that have targeted almost 40 ATMs in Sydney alone, the Fraud Squad says.
Up to a dozen members of the sophisticated gang are believed to have entered the country in recent months, moving between capital cities and attaching skimming devices to ATMs, said Colin Dyson, Commander of the NSW Fraud Squad. They operate under the orders of international ringleaders, who at the same time orchestrate similar scams in other countries. At least 10 ATMs in Melbourne have been used to steal customers' bank card details and more than $1 million, police say.
Sydney has been hardest hit, with police sources saying as many as 40 ATMs have been targeted. The amount of cash stolen is yet to be tallied.
NSW police on Sunday arrested two Romanian nationals after people saw them allegedly installing suspicious devices on an ATM at Avalon, on Sydney's northern beaches. The men, aged 36 and 32, were charged with possessing implements for making false instruments, and face court today. Seven other Romanian men aged in their 20s and 30s have already been charged over the scams - two who faced court in Sydney last week and five in Melbourne.
In recent days, police in the US and New Zealand also prosecuted Romanian nationals over ATM skimming.
"It's a global phenomenon," Detective Superintendent Dyson said. "We also suffer a fair bit of internet fraud from that part of the world, from Eastern Europe and Russia. "It seems they're adept at putting this technology together."
Detective Superintendent Dyson said there had been a rise in ATM skimming since late last year, "Back in 2005 we arrested some Bulgarians that came out here. "There hasn't been a great number of incidents since then, but towards the end of the year we started to see it again."
"The monetary impact is hard to gauge, even for the financial institutions, as its hard to identify [if missing money] is the result of ATM skimming, retail skimming or phishing or internet fraud," Detective Superintendent Dyson said.
Monday, April 13, 2009
HomeATM at Booth 347 at ETA with FIS!
| |||||||||||||||||||||||||
Is that an ATM in Your Pocket?
Editor's Note: And a "REAL" ATM in your pocket can be NYCER yet! (real-time balance inquiries, real time money transfers, real time payments, and a real time saver when it comes to swiping vs. typing! That said, this is a great service from NYCE...
From BTN's John Adams:
Customer knowledge is a cornerstone of relationship building, and NYCE plans to extend balance information to consumers before they go to an ATM via mobile devices—a simple nugget of information the network hopes will attract banks eager to sell convenience to consumers.
NYCE will offer balance inquiries by text message to its financial institution participants as a standard feature of full participation in the NYCE Network.
The text message transactions will be an expansion upon balance inquiries that are available at NYCE Network ATMs, with no additional fees for mobilization. The new Monitise Americas-powered service will allow consumers to use text messaging to request and receive real-time balance information on their primary accounts. The balance inquiries will work for almost all mobile phone users regardless of their mobile carrier or the type of handset they use.
“It’s simple to execute and has no big download,” says Steven Rathgaber, president and COO of NYCE. “The right way to think about it is as an ATM in your pocket, at least from a balance inquiry perspective.”
The prevailing wisdom in mobile banking is balance inquiries are a primary point of entry, and Rathgaber says NYCE is trying to “decommoditize” the function by linking to the NYCE network, which provides consumers with secure, real-time access to their money, offering hundreds of thousands of ATM locations and millions of point-of-sale locations nationwide. Rathgaber would not say how many institutions have taken up the service, which is only a few days old.
A recent survey of North American consumers, commissioned by Monitise Americas and conducted by MaCorr Research1 found that more than 75 percent of consumers say having real-time information regarding their accounts was important. And of those who said they would like to use mobile phones for financial services, more than 90 percent said they are interested in basic information such as account balances.